Cybersecurity & Firewalls
Oct 19, 2026
6 min read
Most FortiGate purchases in Saudi Arabia go wrong in one of two ways. Either the appliance is sized from the number of employees and runs out of capacity once SSL inspection and IPS are switched on, or the hardware is bought without a security subscription and the firewall quietly stops receiving threat updates. Both mistakes are avoidable if you size from your real traffic and decide on licensing at the same time as the hardware. This guide explains how we approach that decision for the FortiGate models we supply, from the FortiGate 30G up to the FortiGate 200F.
Size from traffic and features, not head count
Head count is a weak proxy. Twenty engineers moving large files over a fast fibre link put more load on a firewall than eighty staff using a CRM in the browser. Before choosing a model, collect four facts: the speed of each internet link today and what you expect within the next three years, the number of remote users who will connect over VPN at the same time, which security features you will actually enable, and how many internal segments or VLANs the firewall will route between. Security features matter most. Deep SSL inspection, IPS, antivirus and application control all consume processing capacity, and in a regulated environment you will usually want them on.
Fortinet datasheets list several throughput figures. The headline firewall throughput is measured with inspection switched off and is rarely the number that limits you. The figures to compare are threat protection throughput, which reflects the firewall with its security services enabled, and SSL inspection throughput if you plan to inspect encrypted traffic. Compare those against your internet link speed with headroom to spare, and check the concurrent session and VPN tunnel figures if you run many branches or remote users. Always check the current datasheet for the exact model rather than relying on numbers copied into older proposals.
Small offices and remote sites: FortiGate 30G, 40F and FortiWiFi 40F
The FortiGate 30G (FG-30G) and FortiGate 40F (FG-40F) are desktop units aimed at small offices, retail outlets and remote sites with a single internet connection and a modest number of users. The FortiWiFi 40F (FWF-40F-E-BDL-950-12) combines a 40F-class firewall with built-in Wi-Fi, which suits a small site where a separate access point is not justified. If the site will grow, or coverage must extend beyond one room, a wired FortiGate plus a FortiAP such as the FortiAP 231F (FAP-231F-E) is usually the cleaner design, because access points can be added later and managed from the same FortiGate.
Branches and mid-size offices: 50G to 90G
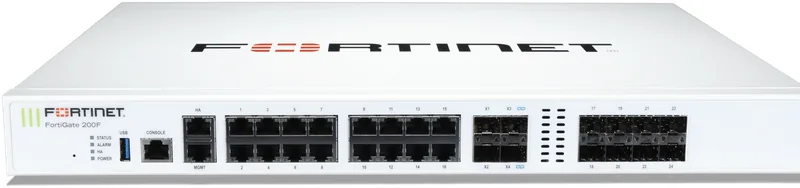
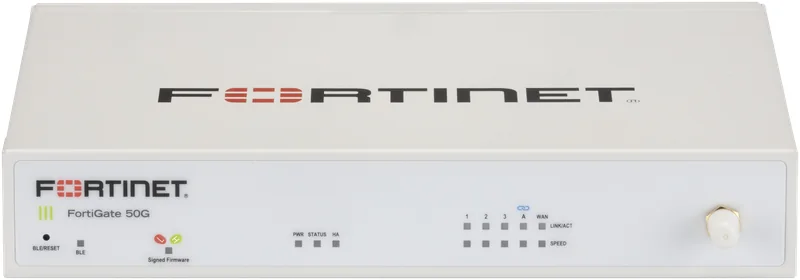
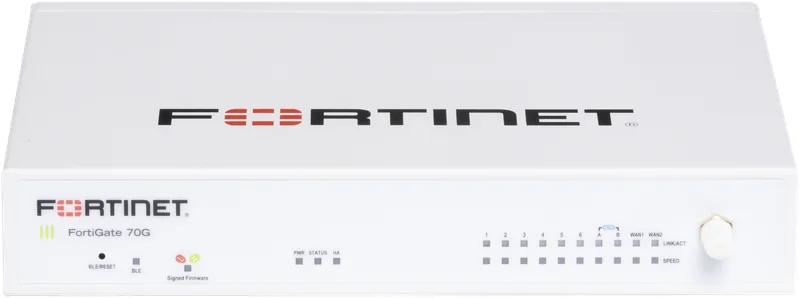
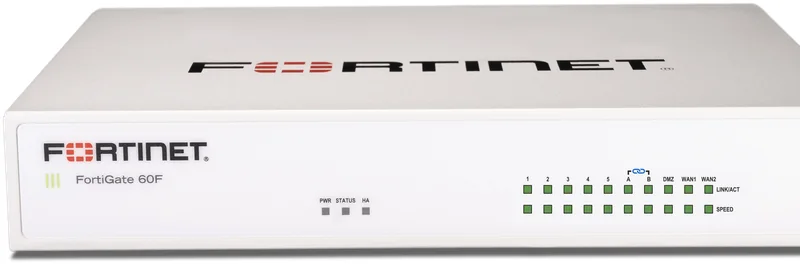
The middle of the range covers most Saudi branch offices and many SME head offices: FortiGate 50G (FG-50G), FortiGate 60F (FG-60F), FortiGate 70G (FG-70G), FortiGate 80F (FG-80F) and FortiGate 90G (FG-90G). The G-generation units are Fortinet's newer platforms and sit alongside the established F-generation models. Moving up the range generally brings more ports and more inspection capacity, and the larger units add options such as SFP ports for fibre uplinks. For a multi-branch network, standardise on one or two models so that configuration templates, spares and renewals stay simple. Larger head offices and data centre edges usually move to the FortiGate 100F or FortiGate 200F, which we supply as 1-year UTP bundles (FG-100F-BDL-950-12 and FG-200F-BDL-950-12).
What the models ending in 1 add
Several models come in pairs: 30G and 31G, 50G and 51G, 60F and 61F, 70G and 71G, 80F and 81F, 100F and 101F. In Fortinet's naming, the variant ending in 1 adds internal storage so logs and reports can be kept on the appliance itself. If you already send logs to FortiAnalyzer or another central platform, the base model is usually enough. If the site has no central logging, the storage model gives you local history for investigations. Licenses are model specific: the FortiCare + UTP renewal for the 60F (FC-10-0060F-950-02-12) is a different SKU from the one for the 61F (FC-10-0061F-950-02-12), so always quote the exact model when renewing.
Bundle, hardware only, or renewal license
Every FortiGate can be bought as hardware alone or as a bundle. Part numbers containing -BDL-950-12, such as FG-60F-BDL-950-12, include one year of Unified Threat Protection (UTP), which combines FortiCare support with FortiGuard security services such as IPS, antivirus and web filtering. Parts ending in -BDL-950-36, such as FG-50G-BDL-950-36 or FG-70G-BDL-950-36, include three years. Hardware-only units like FG-40F make sense mainly for replacements or when a separate licensing plan is already in place. A firewall without an active subscription keeps passing traffic but stops receiving signature updates, which defeats much of the purpose of a next-generation firewall.
Check part numbers carefully. Our catalogue includes three-year bundles for the FortiGate 71F (FG-71F-BDL-950-36) and FortiGate 90F (FG-90F-BDL-950-36) alongside the G-generation 71G and 90G. These are different hardware platforms, so confirm which generation your proposal or tender specifies before ordering.
Choosing one year or three years is mostly a budgeting question. A three-year bundle locks in the subscription with the hardware and removes an annual renewal cycle, which many procurement teams prefer because each renewal otherwise needs its own approval. A one-year bundle keeps the initial outlay lower and suits organisations that budget operating expenditure yearly. Either way, record the expiry date. When the term ends, the matching FortiCare + UTP license renews it, for example FC-10-GT50G-950-02-12 for the FortiGate 50G or FC-10-FG30G-950-02-12 for the FortiGate 30G.
Saudi considerations: NCA ECC and tenders
For organisations subject to the NCA Essential Cybersecurity Controls, the firewall supports several control areas, including network security, event logs and monitoring, and malware protection. In practice that means keeping security services licensed and current, retaining logs your security team or managed provider can review, and controlling remote access. ECC also expects multi-factor authentication for remote access, and FortiToken Mobile licenses, sold in user packs from FTM-ELIC-5 up to FTM-ELIC-10000, add a second factor to FortiGate VPN logins without hardware tokens. For government and semi-government tenders, specify exact part numbers including the subscription term, and require genuine new units with the manufacturer's warranty so support entitlement registers correctly.
Requesting a quotation from Shabackat
If you are unsure which model fits, send us your internet link speeds, approximate user and VPN counts, the security features you plan to enable and whether you have central logging. We will recommend a model and subscription term and return a quotation, with same-day quotes on stocked items. Shabackat supplies genuine new Fortinet products with the manufacturer's warranty, delivers across the Kingdom including Riyadh, Jeddah and Dammam, and offers installation, configuration and support. Contact us on WhatsApp or phone at +966 55 826 9606, or use the quote form on shabackat.sa.