
Cisco vs Aruba Wireless: Picking by Management Model
Both make excellent access points. The decision that matters is how the network is managed and licensed, not which radio is faster.
Read More: Cisco vs Aruba Wireless: Picking by Management ModelThe case for endpoint protection no longer needs making — every organisation has some. The question worth asking is a narrower one: what do you gain by having the endpoint agent, the firewall and the network under one management umbrella instead of buying each on its own merits? For Fortinet that umbrella is the Security Fabric, and the honest answer is that it buys you specific things and not everything.
The firewall still matters, but the traffic it inspects is mostly encrypted and a large part of your workforce is not behind it. Staff work from home and from client sites, they use SaaS applications that never traverse your datacentre, and the device in their hand is doing work that used to happen on a desktop inside the building.
That is not an argument against firewalls. It is an argument that a device needs protection that travels with it, and that what happens on that device should be visible to whoever is watching the network.
Three things, concretely. The first is telemetry: the firewall learns what is running on the endpoint, so a policy can be written about the state of a device rather than only about its IP address. A machine missing a patch or running something it should not can be treated differently on the network.
The second is coordinated response. When something is detected, the endpoint can be quarantined at the network level rather than waiting for someone to notice an alert and act. The value here is time, and time is the thing that decides how far an incident spreads.
The third is fewer consoles. That sounds like a convenience argument, and it partly is. But in a team where one or two people carry security alongside everything else, the number of interfaces they must check daily is a real determinant of whether alerts get looked at.
It does not remove the need for someone to respond. An integrated platform shortens the path from detection to containment; it does not decide what an alert means or whether a quarantine was correct. If nobody is reading the console, integration mostly produces faster automated actions and unexamined logs.
It also does not make single-vendor automatically better. If your organisation already runs a mature endpoint product with good coverage and tuned policy, replacing it purely to gain fabric integration is rarely the right call. Integration is worth most when you are choosing anyway, or when the current tooling is genuinely fragmented.
And it is not a compliance certificate. It helps you produce evidence, which is a different thing from having a control in place.
If you fall under the Essential Cybersecurity Controls, several requirements land directly on the endpoint: malware protection, patch and vulnerability management, event logging, and the ability to show that these are operating rather than merely purchased.
The practical benefit of a single platform here is evidence gathering. Being able to produce, from one place, a picture of which devices are protected, which are current on patches, and what was detected and when, is most of the work an assessment asks for. Ask to see that reporting during evaluation rather than taking it on trust.
Start with visibility, not enforcement. Deploy in a monitoring posture, watch what the estate actually looks like for a couple of weeks, and expect surprises — unmanaged machines, software nobody authorised, devices years behind on updates. Enforcing policy before you have that picture generates a queue of user complaints and a temptation to switch things off.
Then enforce in stages, starting with the controls whose failure modes you understand. Keep a documented exception process from day one, because you will need it and an undocumented one becomes permanent.
On the firewall side, size for inspected throughput rather than raw, as with any next-generation platform. And confirm where any cloud analysis or sandboxing sends data, so the residency question is settled before the design rather than during an audit.
We supply the FortiGate range along with FortiSwitch, FortiAP and the token and web-application products, and can scope a phased rollout against your device count and site list.
Our engineers are happy to walk through your specific requirements and recommend the right approach — no obligation, no generic sales pitch.
The FortiGate 1000F is a 2RU data centre next-generation firewall with 2x 100 GE QSFP28 and 8x…
FG-1000F-BDL-950-12 bundles the FortiGate 1000F next-generation firewall with one year of…
FG-1000F-BDL-950-36 is the FortiGate 1000F platform carrying a three-year FortiCare Premium…
The FortiGate 1001F shares the 2RU data centre platform of the 1000F, including the same 2x…
FC-10-00207-950-02-12 is a one-year Fortinet bundle that pairs FortiCare Premium support with…
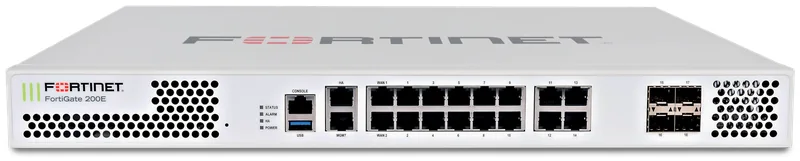
FC-10-00208-950-02-12 renews FortiCare Premium support and the FortiGuard Unified Threat…
Both make excellent access points. The decision that matters is how the network is managed and licensed, not which radio is faster.
Read More: Cisco vs Aruba Wireless: Picking by Management Model
Three capable platforms with genuinely different trade-offs in throughput per riyal, management model and licensing. Here is how to tell which fits.
Read More: Fortinet vs Palo Alto vs Cisco: Choosing a Firewall
Mixed Cisco and Huawei networks work. The problems are always in the same four places, and all four are avoidable at design time.
Read More: Cisco and Huawei Interoperability: What Actually Breaks